
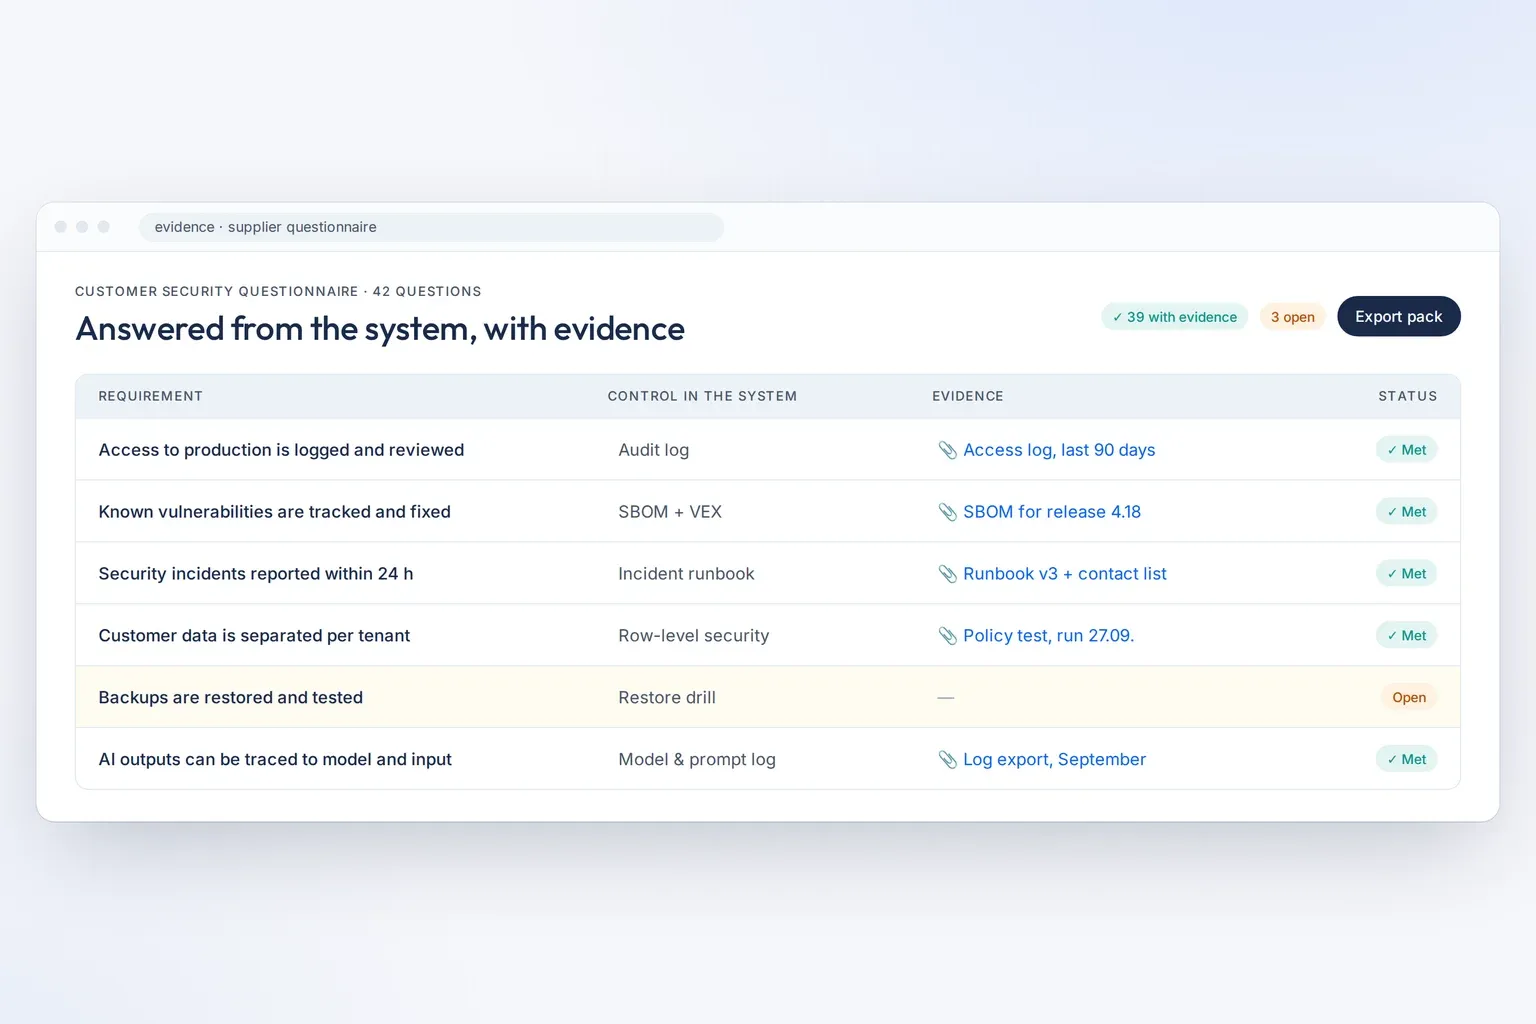
EU rules on security, data and AI increasingly ask the same question: can you show it? We build the answer into your software, so the evidence is produced as the system runs instead of being reconstructed before an audit.
When to call us
- A customer sends a security or AI questionnaire you cannot answer from the system itself.
- A client covered by NIS2 asks you, as a supplier, for security measures and incident contacts.
- You make software and need to prepare for the Cyber Resilience Act: vulnerability reporting has applied since September 2026, the full requirements apply from December 2027.
- Your product uses AI, and you need the documentation and logging the EU AI Act asks for.
What we build
- Requirement to control. A map from each requirement to the part of the system that meets it, and to the evidence that shows it.
- Controls in the code. Audit logs, retention rules, access control and tenant isolation, versioned records, and logging of AI inputs, outputs and model versions.
- Evidence and documentation. Software bills of materials, vulnerability handling and technical documentation generated from the system, so they stay current.
What we do not do
We are engineers, not lawyers or auditors. Your counsel or data protection officer decides what the rules mean for you; we make the software able to prove it.
Our own example
Cjenik turns a Croatian legal obligation — publishing price lists — into a short workflow, and keeps an unchangeable archive of every published version.
Tell us which rule or questionnaire is on your desk.